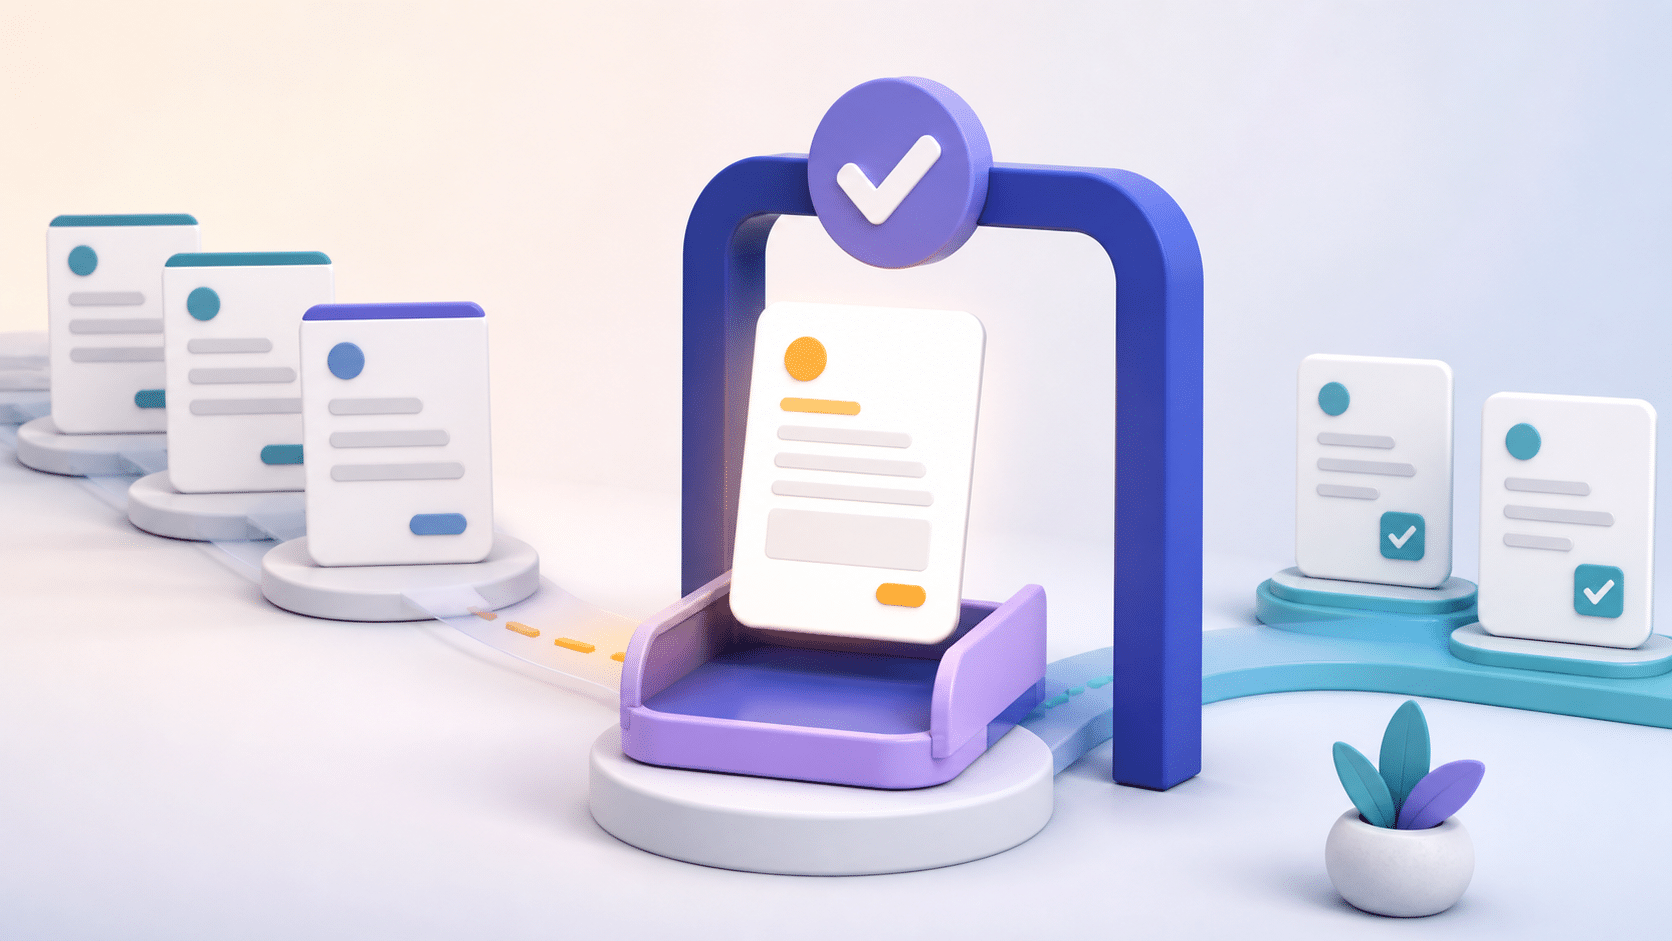
A form submission can start an important decision without being the place to finish it. An access request may need identity checks. A refund request may need account history. A vendor inquiry may need procurement review. An abusive message may need a safer handling path. In each case, the useful automation is the part that prepares a clear review record. The approval still belongs to a person with authority to make it.
This distinction protects visitors, staff, and clients. It also keeps a WordPress workflow honest. Sentient Forms can prepare review aids and recommendations for supported submissions. It does not prove that a business approved a request or perform that business approval for you.
Approval is a business step, not a form setting
Start by naming the decision that changes someone’s outcome. “Approve account access,” “issue a refund,” “send this customer response,” and “escalate this threat” are decisions. “Summarize the submission” and “suggest the next owner” are review aids.
That boundary matters when a request looks routine but is missing context. A customer may ask for a refund after a partial delivery. A new contractor may request access before a manager has confirmed the engagement. A message may sound urgent without containing enough facts to act safely. Make the human decision visible instead of letting a helpful-looking note quietly become the decision.
Separate recommendations from authority
Give each workflow two fields that cannot be confused: the recommendation and the final decision. A recommendation can say that a request appears to need billing review, that a reply draft needs policy or manager review, or that the evidence is incomplete. The final decision should record who approved, declined, or escalated it and when.
This is also a better operating habit for agencies. A client should be able to see whether the team acted on the form entry, rather than assuming an internal suggestion changed access, money, a vendor relationship, or customer terms.
Mark the decisions that must pause for a human
Do not begin by trying to classify every form. Pick the cases where a mistaken action would be hard to explain or reverse. Access requests are a practical first example. A request may contain the right name and email address, yet still need a manager to confirm the person, the scope, and the expiry of access. Use the same pause for unusual refunds, account changes, sensitive vendor requests, and customer replies that make commitments.
Your access-request process should say what evidence the approver needs, who may approve, and what happens when that person is unavailable. A submission alone is not evidence that the requested action is authorized.
Give every decision an owner and a fallback
An approval queue with no owner is only a slower inbox. Name the primary approver, the backup, and the time when a request should move to a different queue. Keep the fallback concrete. “Ask the operations lead” is less useful than “If the billing owner is unavailable, hold the request and assign it to the operations lead for review.”
Add that rule to the form’s definition of done. The request is complete when the business decision is recorded, the visitor receives the appropriate response, and the team can find the record later. It is not complete when a suggestion appears in an admin screen.
Give reviewers the evidence they need
Reviewers should not have to reconstruct the case from an email thread and a vague note. Keep the approval record short enough to scan, but include the facts that change the decision.
| Decision type | Review record should include | Human action |
|---|---|---|
| Access request | Requested scope, requester identity evidence, manager or client context, expiry request | Approve, decline, or request verification |
| Refund or account exception | Order or account reference, stated issue, relevant policy or account context, missing facts | Approve, decline, escalate, or ask a follow-up question |
| Consequential customer reply | Draft response, facts relied on, promises or deadlines in the draft, unresolved questions | Edit, send through the normal channel, or replace the draft |
| Abusive or threatening message | Original message location, safety concern, exposure limits, named escalation path | Escalate under the team’s safety procedure |
The Sentient Forms Action Library can help teams prepare reviewable summaries, routing recommendations, and other focused notes. Use that output as a starting point for review. Do not let a confidence label stand in for the missing business facts.
Keep WordPress permissions narrow
Approval authority and WordPress access are related, but they are not the same thing. WordPress roles group capabilities, and capabilities control what an account may do in the site. Review the actual capabilities needed for the workflow, then avoid granting broader access simply because someone needs to review a form entry. The WordPress roles and capabilities guidance is a useful reference when you document who can view, edit, or publish a related change.
Keep the business approval rule outside the role name. An Administrator may be able to change site settings, but that does not automatically make that person the right approver for a client refund or a vendor commitment.
Treat abusive messages as a safety case
Abusive, threatening, or unsafe messages should not be pushed into an ordinary reply queue. Limit who needs to read the content, preserve the original entry according to your own process, and define who decides whether to respond, block future contact, or escalate outside the team. The goal is staff awareness and safe handling, not an automatic judgment about a person.
For a practical starting point, use the guidance on handling abusive WordPress form messages alongside the Toxicity and Safety Review action reference. Keep the final response or escalation with the people who own that responsibility.
Review reply drafts before they become promises
A good draft can save time. It can also accidentally promise a refund, access change, deadline, or exception that nobody approved. Put review instructions beside the draft: what facts must be checked, which phrases require an approver, and which normal sending channel the team should use after approval.
The Suggested Reply and Next Best Action is deliberately a draft layer. Edit it for the actual case, then let the authorized person decide whether it should be sent.
Test the approval path before relying on it
Run a controlled test with a harmless sample request. Confirm where the record appears, who receives it, what the backup owner does, and how the final decision is recorded. Test the unavailable-approver case too. A clean recommendation is not enough if the request can sit unnoticed or the team cannot tell who made the final call.
Start with one high-risk form and one decision rule. Once the team can explain the evidence, authority, fallback, and record, the workflow is ready for a real pilot.
No. It can prepare review aids or recommendations for supported form submissions. Your authorized staff and business process make and record the approval decision.
Show the original request or its trusted location, the facts that affect the decision, the recommendation if one exists, the named approver, and a clear place to record the final decision.
Use it as a draft for human review. Check the facts, commitments, tone, and any policy-sensitive language before an authorized person sends a response through the normal channel.
Choose one form where a person already makes a consequential call, then build the review record around that real decision.